01 / 05
ISO/IEC 27001
Understand information security management systems, risk treatment, control ownership and the documentation commonly needed for readiness and continual improvement.
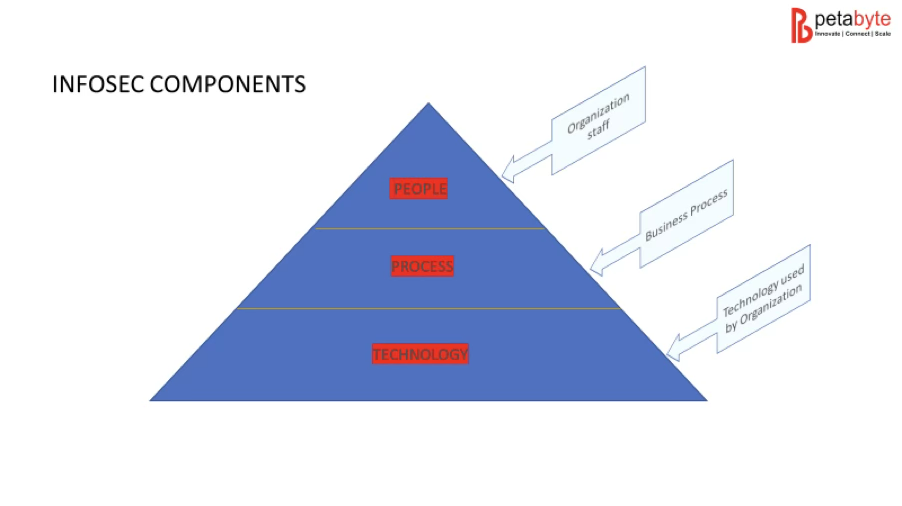
ISO/IEC 27001 is the international standard for an Information Security Management System (ISMS). It provides a structured framework for managing information security risks and protecting the confidentiality, integrity and availability of information through people, processes and technology.
Certification can demonstrate an organisation's commitment to information security and help build confidence among customers, partners and stakeholders.
The standard provides a systematic way to establish, implement, maintain and continually improve an ISMS. It is designed to help organisations identify information security risks and manage them through appropriate, documented controls.
A globally recognised specification for establishing, maintaining and continually improving an information security management system.
Guides organisations in identifying, assessing and treating information security risks according to their context and risk criteria.
Addresses information security through the combined management of people, policies, processes, technology and organisational responsibilities.
Focuses on preserving the confidentiality, integrity and availability of information throughout its lifecycle.
Can be applied by organisations of different sizes and sectors, with the ISMS scope and controls tailored to their context.
Select each principle to explore what it means and how it applies to protecting business information.
Information should only be accessible to authorised people, systems and processes. Appropriate access permissions, identity controls and data protection measures help reduce unauthorised disclosure.
Access control, least privilege, information classification and protection of sensitive data.
An effectively implemented ISMS can support stronger information security practices while giving leadership a structured way to manage risks, responsibilities and improvement priorities.
Helps address risks associated with cyberattacks, data breaches, unauthorised access and human error through systematic controls.
Certification, where achieved, can differentiate an organisation and provide additional assurance to customers and business partners.
Helps organise security controls and evidence that may support relevant legal, contractual and regulatory obligations.
Proactive risk management can help reduce the likelihood and impact of incidents and associated financial losses.
Demonstrates a structured commitment to information security and helps build confidence among customers and stakeholders.
Establishing an ISMS involves understanding risk, selecting appropriate treatments, managing the system and improving controls as the organisation changes.
Identify information assets, threats, vulnerabilities and potential impacts using defined risk assessment criteria.
Select appropriate risk treatment options and determine the controls needed to address identified risks.
Define scope, policies, roles, procedures, evidence and management processes required to operate the system.
Review performance, evaluate controls, conduct internal audits and track corrective actions and continual improvement.
Consultancy activities can help your organisation understand its current position, identify gaps, establish required processes and prepare for an independent certification audit.
Review existing information security practices against applicable ISO/IEC 27001 requirements to identify areas that may require improvement.
Identify and evaluate information security risks, document findings and develop a risk treatment plan aligned with organisational priorities.
Support the development of appropriate ISMS policies, procedures, control documentation, responsibilities and implementation activities.
Help personnel understand information security responsibilities, relevant policies, secure practices and their role in supporting the ISMS.
Assist with audit preparation, evidence organisation, corrective action tracking and readiness activities within the agreed consultancy scope.
Documentation should reflect the organisation's scope, risks, processes and applicable standard requirements. The following items are important examples, not an exhaustive list.
Keep policies, risk records, control decisions and audit evidence consistent with the actual operation of your information security management system. Specific documented information depends on the applicable requirements and organisational context.
Any organisation managing valuable, sensitive or business-critical information can consider an ISMS. The scope and controls should reflect its specific assets, risks and operational requirements.
Banks, insurers and investment firms protecting financial and customer information.
Hospitals, clinics and medical research organisations handling sensitive health data.
Software companies, cloud providers and technology businesses managing client data.
Businesses protecting proprietary designs, intellectual property and operational data.
Public sector organisations managing confidential citizen and administrative information.
Discuss your current security posture, ISMS scope, documentation needs and readiness priorities with Petabyte.
ISO/IEC 27001 consultancy and readiness support do not themselves confer certification. Certification is determined by an independent certification body following its audit process. Actual scope, deliverables and timelines depend on the organisation and agreed engagement.